Key takeaway (TL;DR) The weakest link has two very different meanings in systems engineering. An unintended technical defect can become a disastrous point of failure, while a deliberately designed sacrificial element can protect the system as a whole. JVDS emphasizes that resilience in high-concurrency digital architecture and interaction design is not about pursuing an impossible promise that nothing will ever break. Circuit breaking, rate limiting, local draft storage and controlled partial degradation trade a contained local loss for the protection of core assets and essential business operations.
1. The wisdom of sacrifice: three physical examples of protective failure
The history of mechanical and electrical engineering shows that, under destructive overload, deliberately allowing one part to fail can be the means of protecting what matters most.
A layered defense model for sacrificial design and system resilience
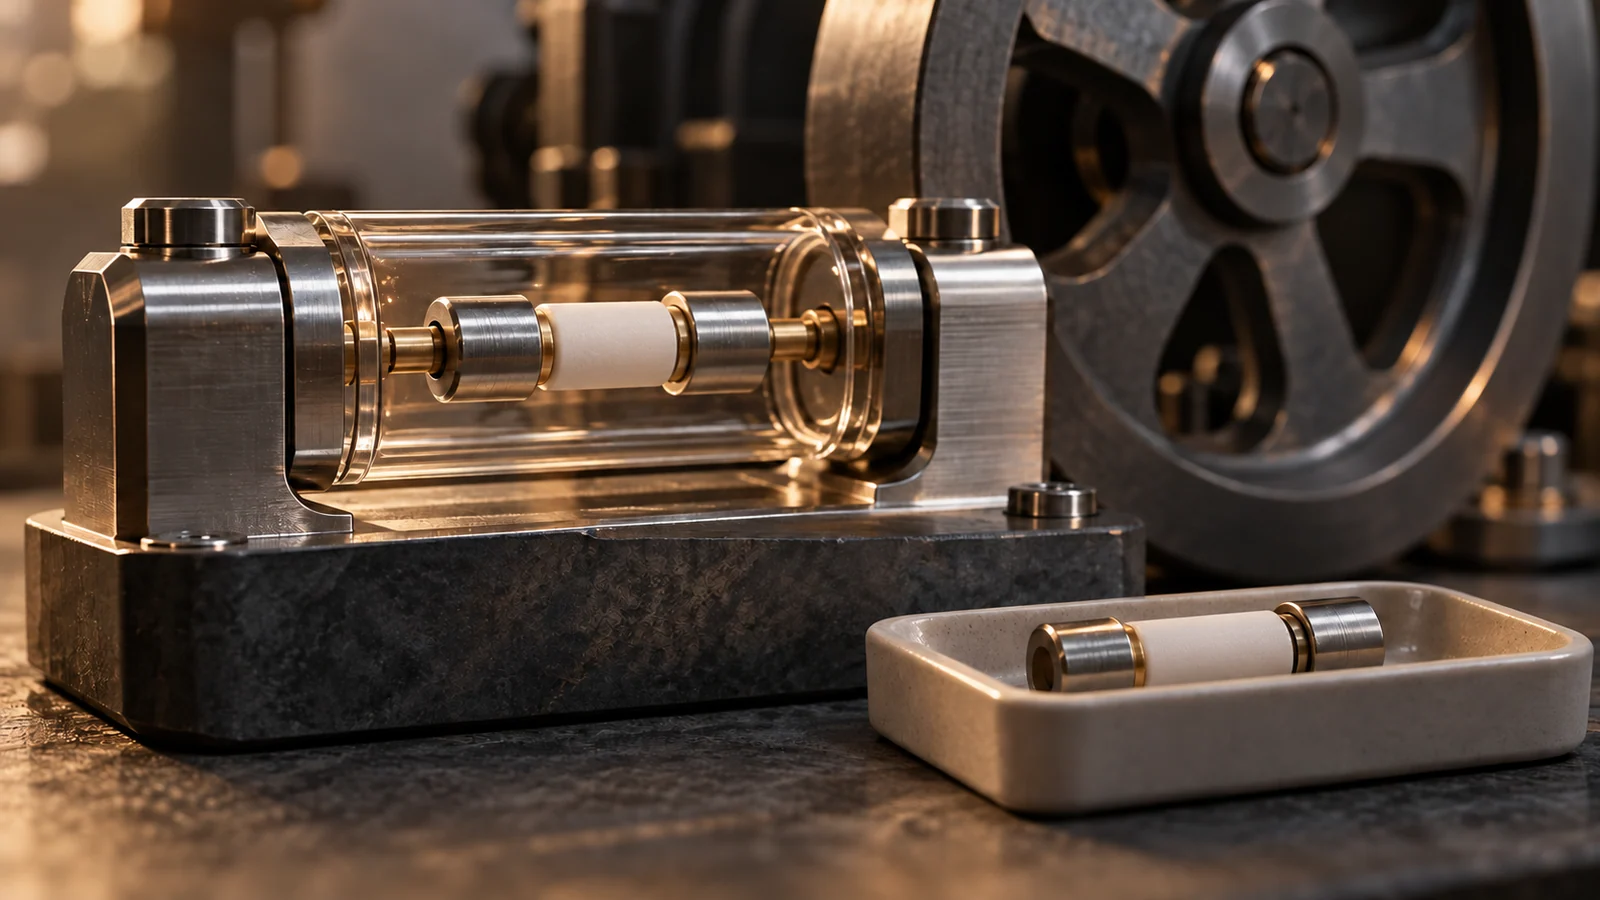
- Layer 1: deliberate disconnection — the electrical fuse. A low-melting-point component opens during an overload, potentially within milliseconds. Its sacrifice breaks the circuit to prevent cascading electrical damage and the spread of fire.
- Layer 2: controlled rupture at a threshold — the sprinkler glass bulb. Heat causes a temperature-sensitive liquid to expand and break a small glass tube. This calculated failure acts as a trigger that releases pressurized water.
- Layer 3: energy absorption through plastic deformation — vehicle crumple zones. Front and rear structures fold under impact to absorb kinetic energy, preserving space around the more rigid passenger compartment.
- Layer 4: service circuit breaking and degradation — distributed software. When a secondary interface becomes overloaded or times out, circuit breaking and rate limiting stop calls to it, reserving computing capacity and database connections for core payment transactions.
- The electrical fuse: breaking the circuit to stop cascading destruction. In the example described here, a fuse uses a low-melting-point lead-antimony alloy. During a severe overload or short circuit, it melts first, potentially within milliseconds, interrupting the circuit to protect an expensive precision motor and prevent fire. Replacing a fuse with a thick copper wire that will not melt defeats that protection and can expose the building's electrical system to catastrophic damage.
- The automatic sprinkler's glass bulb: failure as activation. A closed ceiling sprinkler holds its sealing plug in place with a small glass bulb filled with a heat-sensitive liquid. During a fire, the liquid expands as the surrounding temperature rises until the bulb breaks. This damage is not an accident: it is the designed trigger that releases pressurized water.
- Modern vehicle crumple zones. Mid-twentieth-century vehicle design often favored rigid all-steel structures. A frame could remain relatively intact in a collision while occupants suffered fatal deceleration. Béla Barényi helped establish the separation of a vehicle into deformable front and rear zones and a protected passenger cell. The sacrificial zones deform extensively to absorb kinetic energy, while a strong passenger compartment protects occupants. The principle is to allow sufficient local deformation to improve protection of the core.
2. From physical engineering to software circuit breakers
In highly available digital systems and web platforms, the weakest-link principle becomes an important foundation of distributed-system design.
- An API circuit breaker in the style of Netflix Hystrix. On a large streaming or e-commerce platform, a nonessential recommendation service can stall because of network problems. Thousands of requests may then occupy the available thread pools and trigger a cascade that reaches essential payment infrastructure. Middleware acts as a digital fuse: once the error rate crosses a threshold, it stops calling the secondary service and quietly returns static fallback data, reserving 100% of scarce server computing capacity for core payment and settlement flows.
- Protective input recovery and local draft snapshots. During an hour-long form-filling task, a user may encounter a browser crash, power failure or unstable network connection. Millisecond-level front-end snapshots in memory and LocalStorage preserve the draft locally. Even if a submission request fails, the user's essential input remains available for one-click recovery.
3. A four-dimensional matrix for sacrificial design in systems and interfaces
The following matrix helps engineering and experience teams place protective mechanisms appropriately in interaction design and large administrative systems.
| Evaluation dimension | Frequent core functions or assets | Occasional but necessary functions or assets | Redundancy, false functionality or empty styling |
|---|---|---|---|
| High concurrency and protective rate limiting | During extreme traffic peaks, protect payments and asset-security operations first, while gracefully degrading peripheral features. | At 95% system load, show a considerate waiting page with a countdown and a message such as “12 visitors are ahead of you.” | Assume the system is indestructible, omit circuit breakers and rate limits, and allow a traffic surge to produce widespread 502 failures. |
| Form data and interrupted-session protection | Cache local drafts silently during input and use an offline queue when network connectivity fluctuates. | After an unexpected crash or refresh, show a clear “Your unsubmitted draft has been restored” banner. | Erase all 30 fields a user has completed as soon as a submission times out. |
| Permission safeguards and risk containment | Temporarily freeze an account and require secondary SMS verification when brute-force attempts or unusual remote access are detected. | Use a CAPTCHA after repeated failures and clearly display the remaining retry allowance. | Provide no security thresholds, allowing credential-stuffing scripts to attack until core user data is stolen. |
| Error isolation in long workflows | Use row-level fault tolerance in a batch upload: accept 98 valid records and flag only the two incorrect ones. | Let users correct those two rows in place and resubmit them independently. | Reject an entire spreadsheet of 1,000 records because one nonessential optional field has the wrong format. |
4. JVDS's resilience engineering practice
In JVDS work on financial-technology platforms, international supply-chain hubs and industrial SaaS systems, our resilience standard is to anticipate failure and provide controlled fallbacks.
- Define the experience of graceful degradation. We distinguish essential business functions from secondary experience enhancements. Under severe network conditions or a back-end circuit break, the system should deform predictably, like a vehicle's crumple zone. It temporarily removes high-frame-rate animation, live personalized recommendations and large high-resolution imagery, falling back to a lightweight, robust native data-entry panel that keeps the business operating.
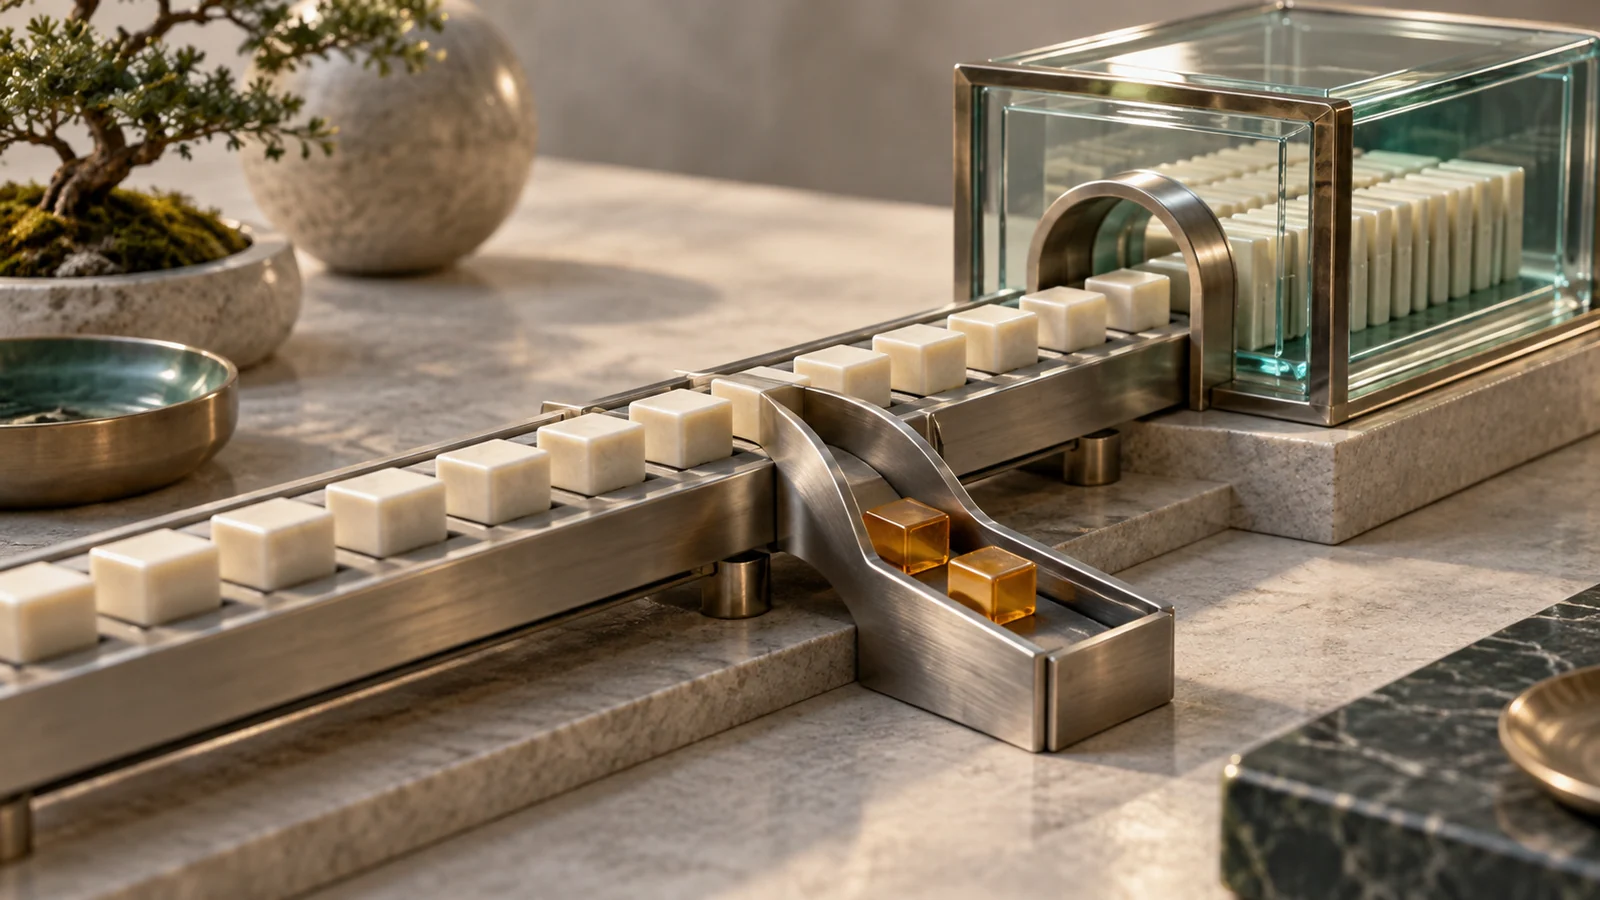
- Redesign interactions around row-level isolation. For large data imports and complex configuration, we reject an all-or-nothing response to every minor error. Local isolation allows valid records to take effect first. Blocked records appear with restrained amber row highlights in a side drawer, with contextual actions for correcting each issue.
- Run interaction stress tests with chaos engineering. Before launch, we work with developers in a production-simulation environment to introduce localized network loss, API timeouts and temporary database interruptions. We verify the interface's response: did the failure cause a duplicate charge, did the user receive a definite diagnostic clue, and could the interface reconnect within one second after service recovery? Explore our design portfolio for work that combines usability with system resilience.
5. Frequently asked questions
Q1: If a weak link can protect a system, should we deliberately build secondary modules badly?
No. Protective sacrificial design is fundamentally different from poor engineering. A protective element must disconnect in a precisely controlled way under predefined extreme conditions. The article's simplified fuse example contrasts a 15-ampere failure threshold with normal operation at 5 amperes: it should not trip repeatedly during ordinary use. Frequent errors and bugs in everyday secondary functions indicate a development-quality failure, not engineering intelligence.
Q2: How should the interface treat users who are rate-limited during an attack or traffic surge?
Do not show a blank page, an unexplained JSON error or only “System busy.” Instead, explain the peak demand honestly, such as “Many people are visiting right now. We are keeping your place in the queue.” Give a clear expected wait, such as eight more seconds. Preserve prior input and session state so users do not fear that an unstable system has caused a loss of money or work.
Q3: How can we judge whether a protective software design is effective?
Review three measures. Blast-radius containment: does a local failure remain isolated from essential operations? Core survival rate: do core transactions and persisted data remain fully intact under extreme overload? Mean time to recovery (MTTR): after the external disruption ends, can the system return automatically from partial degradation to normal operation within seconds?