Key Takeaway (TL;DR)
Defensible Space originated as a classic theory of crime prevention and order in urban planning and architecture. It argues that safety depends less on high walls and fences than on clear territorial boundaries, unobstructed everyday natural surveillance, and visible signs of ongoing care and maintenance. Applied to digital collaboration platforms and enterprise SaaS, confused permissions, the tragedy of the commons, and uncontrolled collaboration arise precisely because digital assets lack clear ownership and transparent traceability. JVDS advocates transparent spaces of responsibility in enterprise interaction design, giving ownership boundaries, actions visible feedback, and management a human touch.
1. The Origins of Defensible Space: Newman and the Mechanisms Behind Broken Windows
In the 1970s, architect Oscar Newman's long-term research into crime rates across different types of New York public housing revealed a striking pattern:
- Robbery and vandalism were frequent in high-rise public housing with enclosed long corridors and large lobbies lacking a sense of private ownership.
- In nearby low-rise developments with similar population density but individual courtyards, bright open windows, and clear entry paths, crime rates fell dramatically.
Newman proposed Defensible Space: physical layouts directly shape behavior and territorial psychology. Its core pillars comprise three dimensions:
1.1 Territoriality: Establishing “This Is My Space”
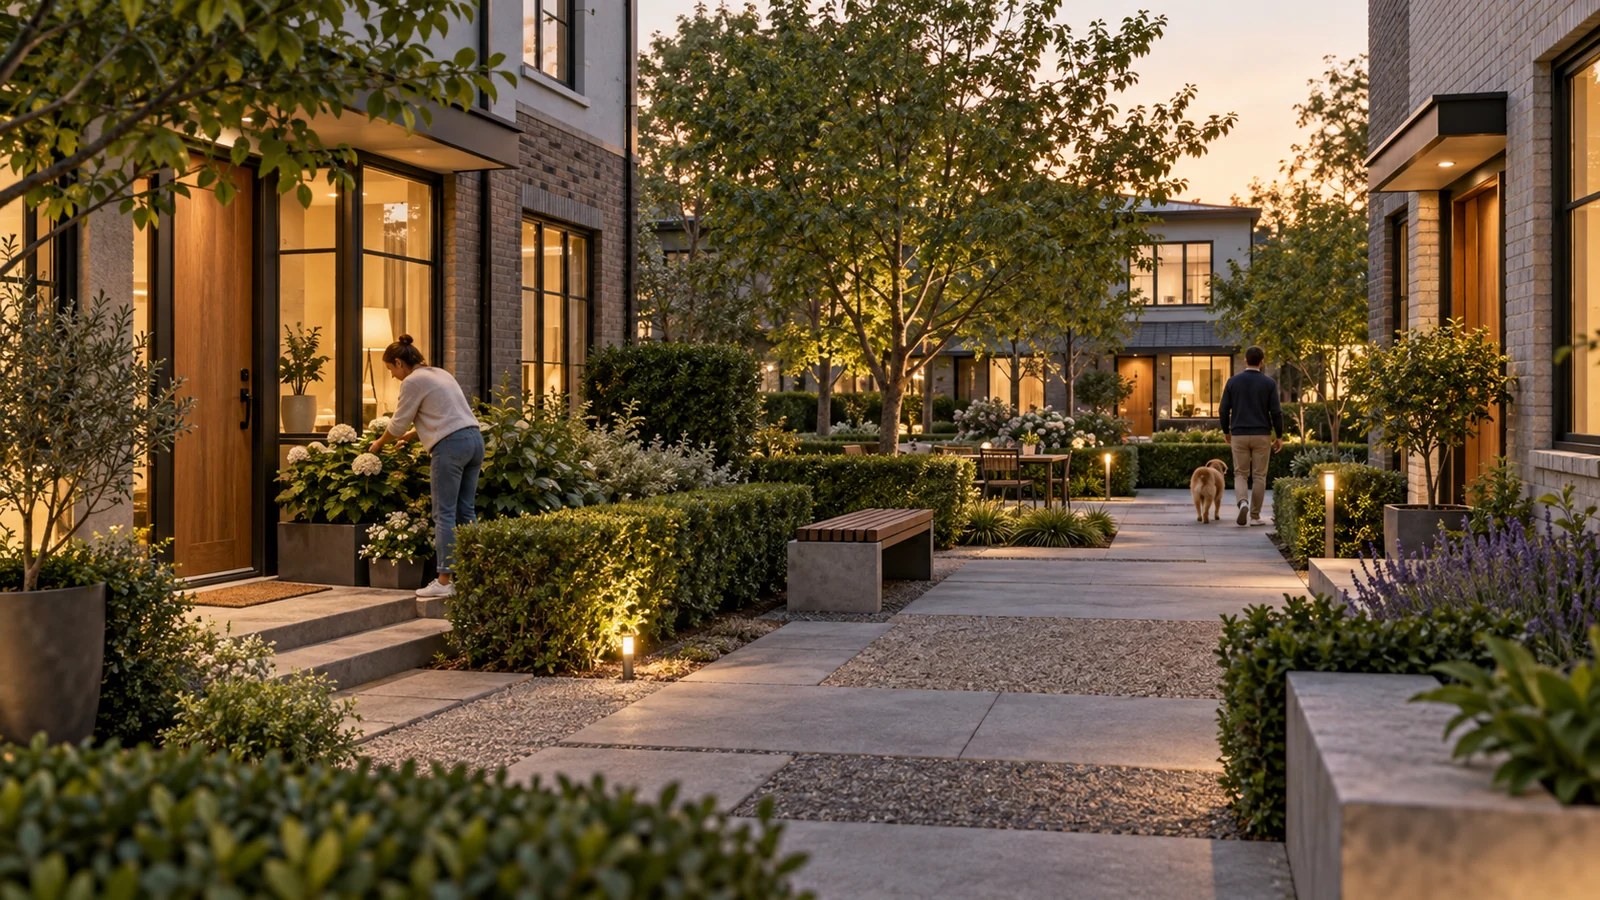
Humans have an innate territorial-defense instinct. Ambiguous boundaries, such as a large neglected plot that belongs both to residents and the municipality, often produce a Tragedy of the Commons: everyone may use it, but no one accepts cleaning or repair responsibilities. Low walls, hedges, and subtle paving changes distinguish private, semi-private, semi-public, and public areas, immediately activating a sense of ownership.
1.2 Natural Surveillance: The Passive Deterrent of Eyes on the Street
Jane Jacobs emphasized Eyes on the Street in The Death and Life of Great American Cities. Defensible space does not mean stationing armed guards in every corner. Orient doors and windows toward shared paths, place benches at intersecting sightlines, and provide bright, even nighttime lighting so ordinary neighborhood activity naturally covers the environment. Potential offenders who feel visible to others are strongly discouraged.
1.3 Image and Milieu: Counteracting the Broken-Windows Effect
Clean, flat doormats, trimmed plants, and freshly cleaned mailboxes silently communicate: “People continue to live in, love, and carefully maintain this space.” An unrepaired window or uncleaned graffiti instead suggests abandonment and loss of control, quickly attracting further damage.
2. From Physical Neighborhoods to Digital Spaces: Territorial Confusion in Collaboration Software
Employees move daily among platforms such as Feishu, DingTalk, Slack, Jira, and Notion. Many contain a severe digital tragedy of the commons:
- Ghost folders and zombie documents: Cloud drives accumulate thousands of items named “New folder (2)” or “Unarchived assets.” No one dares delete them, and no one maintains them.
- Permission black holes and blame: A critical production configuration is accidentally changed, but the audit log says only “Modified by shared administrator account,” breaking the chain of responsibility.
- Indifference and collaboration islands: Departments defend their own territories within the same platform, cannot see one another's work context, and lack shared community identity.
Digital interfaces contain no real bricks or concrete, but users' needs for data ownership, collaborative territory, and safe distance are no different from those in the physical world.
3. A Comparison Matrix for Digital Defensible Space
Healthy territorial mechanisms in enterprise collaboration and organizational platforms must distinguish constructive protection from excessive fragmentation:
| Territorial level | UI/UX implementation and mechanisms | Team security and collaboration efficiency | Implementation traps |
|---|---|---|---|
| Frequent core territorial awareness Transparent rights and responsibilities | • Keep organization identity and membership labels visible at the workspace top. • Explicitly show asset creators, owners, and last-maintained times. • Provide precise multidimensional RBAC inheritance and visual authorization dashboards. | Eliminate management blind spots, establish strong asset ownership, and prevent risks from shared accounts. | Make permissions so opaque that users cannot understand denied access or find a clear request route. |
| Infrequent necessary oversight Audits and visible activity | • Multidimensional Activity Audit Logs for asset changes. • Live Presence Cursors in collaboration. • Watermark notices and risk warnings before sensitive-data exports. | Establish asset-compliance safeguards; moderate transparency encourages self-discipline and reduces speculation and distance. | Adopt extreme surveillance, requiring employees to keep cameras on all day and undermining privacy and trust. |
| Redundant, misguided barriers Departmental fragmentation | • Layer barriers between departments with no cross-domain search. • Require offline approval from top executives for every ordinary shared folder. • Use aggressive inaccessible dialogs and intimidating red warnings. | Destroy organizational agility and drive employees to exchange unencrypted files in private WeChat groups, creating greater security risks. | Equate defensible space with isolated fortified territories, turning collaboration software into a medieval stronghold. |
4. JVDS' Method for Implementing Digital Defensible Space
In enterprise cloud platforms, collaboration workbenches, and asset-management UI/UX, JVDS proposes governance that makes responsibilities visible and collaboration responsive:
[JVDS Digital Territory Governance Model]
Visualize boundaries → Make responsible individuals explicit → Share awareness of activity → Complete permission-transfer loops
- Territory Demarcation System: At the top architectural level, abandon an undifferentiated flat tree. JVDS introduces three visual metaphors: enterprise public hall → departmental semi-private space → personal private workspace. Subtle warm/cool background differences, padding levels, and border textures let users perceive the area's openness and their communication responsibility within 0.1 seconds of entering.
- Living Metadata Architecture: Eliminate lifeless file lists. Every core business-asset card must dynamically aggregate gardener indicators: the responsible person's actual avatar, online state, update frequency over the past seven days, and interaction likes. Digital assets become more than cold bytes, conveying the warmth of attentive ownership.
- Gentle Natural Surveillance: Introduce lightweight digital footprints in shared documents and boards. When a colleague views or edits a configuration row, a gentle breathing highlight and small avatar marker appear there. This shares progress while respectfully reducing accidental deletion risks from hidden activity.
5. Frequently Asked Questions (FAQ)
Q1: Do pure tools such as design applications or code-hosting platforms also need defensible space?
Very much so. Figma's worldwide success is substantially attributable to getting digital defensible space right. In the earlier Sketch era, designers worked privately on local files, keeping assets in closed rooms. Figma introduced Multiplayer Presence and ownership of shared component libraries, turning design files into transparent public squares. Seeing one another working on the canvas stimulates collaborative creativity while naturally discouraging low-level shirking and malicious overwrites.
Q2: How can operational transparency be balanced with employee privacy?
Be transparent about assets and respectful toward people. Natural surveillance concerns changes in work objects, such as who modified a contract clause and when, not intrusion into personal behavior through keystroke monitoring, screenshots, or screen recordings. Work-deliverable transfers must be fully traceable; personal daily communication and unpublished private drafts must receive robust privacy protection.
Q3: How can we tell whether collaboration permissions are safe and orderly or rigid and suffocating?
Observe cross-departmental access-request turnaround and asset-abandonment rates. If a new employee can request a neighboring department's general technical document in one click and receive temporary read-only access within ten minutes, while the document remains well maintained, governance is healthy. If accessing an interface requires four days of approval and three vice presidents' signatures, driving people to copy unencrypted code on USB drives, the defense has turned against the business. Explore the JVDS team's classic design portfolio to see how high security and smooth operation can coexist.